AO3 Down: Security Incident Has Kept Archive of Our Own Offline Since October 29, What Is Confirmed and What Businesses Should Learn
AO3 has been offline since October 29, 2026, after its operator found evidence of a security incident. Here is what is confirmed, what is not, and the recovery checklist for any business that depends on a website.
Where Worldwide
On this page 8 sections
AO3 (Archive of Our Own), one of the largest fan fiction libraries on the internet, has been offline since October 29, 2026, and the nonprofit behind it says it found evidence of a security incident. The fan fiction is not why this matters to a business: what matters is that a site first listed as down for maintenance is still down more than a week later, and its operator cannot yet say whether the user database was taken.
AO3 is run by the Organization for Transformative Works (OTW). AFP reports that the site has more than 11 million registered users and nearly 18 million works. AO3 is offline, so those figures could not be checked against the site itself.
Is AO3 down? What happened and when
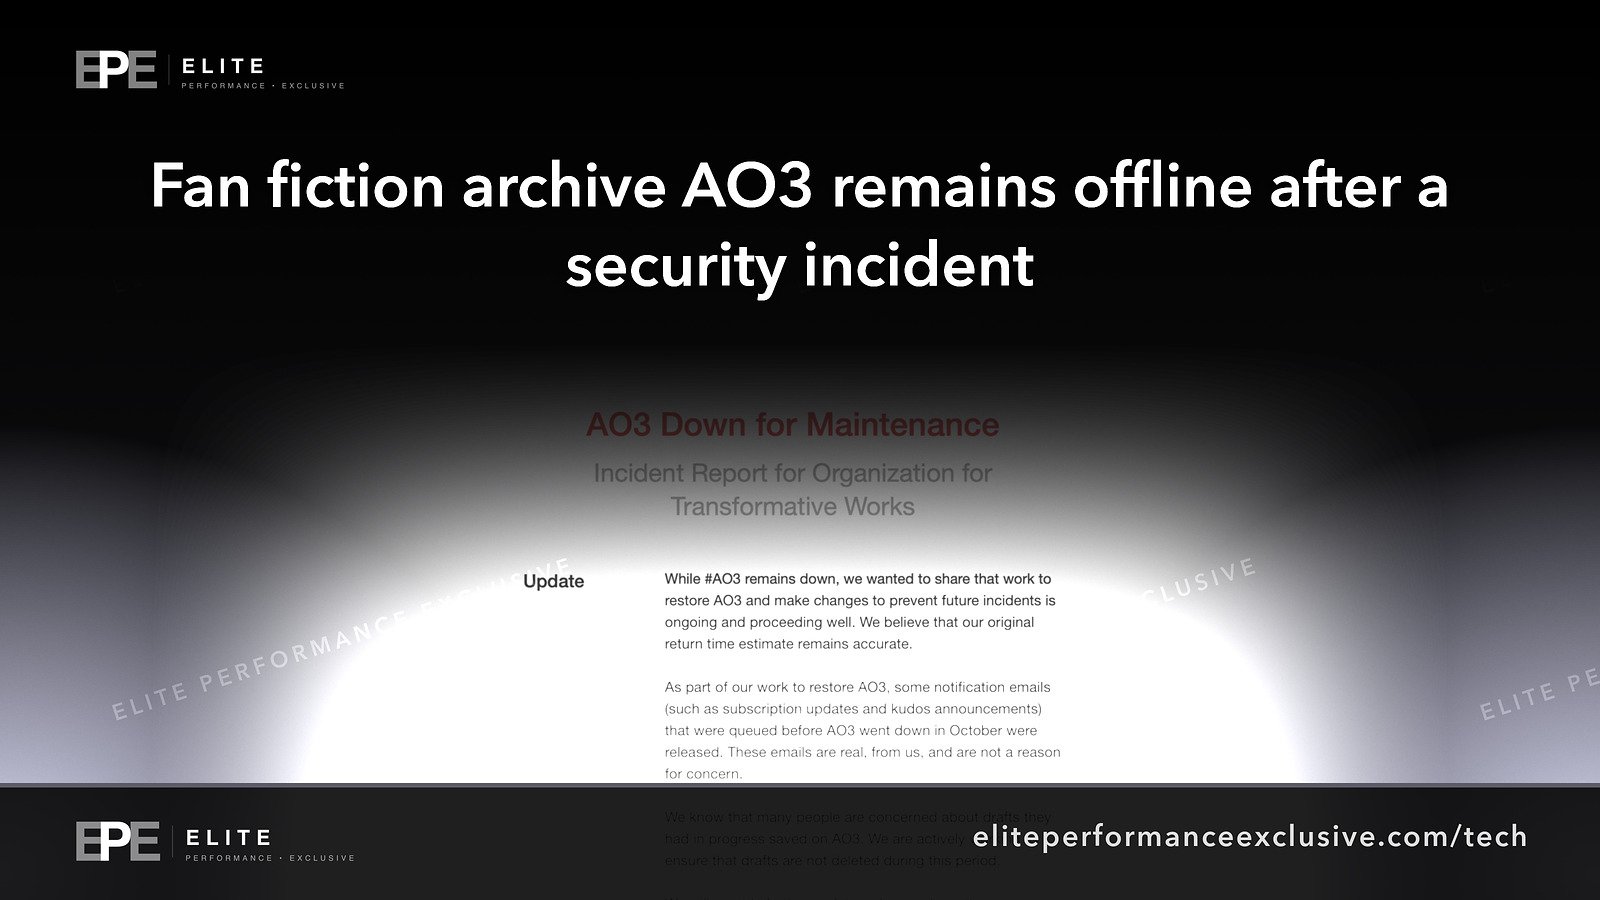
Yes. As of November 8, 2026, OTW's status page lists Archive of Our Own as "Major Outage" and the incident as unresolved. This timeline comes from that page, in UTC.
| Date and time (UTC) | What OTW posted |
|---|---|
| Oct 29, 07:13 | "AO3 is down for maintenance." |
| Oct 29, 09:03 | Maintenance expected to take at least 12 hours |
| Oct 29, 17:41 | Restoration estimated at around 2 weeks, possibly up to 4 |
| Oct 30, 01:27 | "We detected evidence of a security incident on AO3" |
| Nov 6, 00:00 | Work is "ongoing and proceeding well"; the original estimate "remains accurate" |
Two to four weeks from October 29 works out to roughly November 12 to November 26. That is our arithmetic: OTW has not given a date.
What is confirmed about the AO3 security incident
Everything in this list is OTW's own account. We found no outside investigator's report.
- OTW detected evidence of a security incident and is keeping AO3 down while it investigates.
- OTW says no AO3 data has been deleted, and that works, bookmarks and kudos are safe.
- The database may include usernames, email addresses, IP addresses and hashed passwords.
- AO3 does not collect real names, so OTW says none could be exposed.
- Donor information sits in a separate system "never linked to AO3," and OTW says it was not exposed.
- The site may come back in a degraded or read-only state, and could be taken down again during recovery.
What is not known about the AO3 hack
- Whether the user database was stolen. OTW's words: "we currently don't believe that the user database was stolen, we are also unable to rule it out."
- What kind of attack this was. News headlines, including AFP's, say cyberattack. OTW says "security incident." Its status updates do not name an attack type, an attacker or the way in, and do not mention ransomware or a DDoS attack.
- Whether the maintenance and the incident are linked. The first updates say only maintenance, and OTW has not said whether the incident caused the shutdown.
- What is being changed, and the return date. OTW mentions "changes to prevent future incidents" without details.
AO3 password: what to do if you have an account
OTW recommends changing your password on any other site where you used the same one. It says passwords are stored with industry-standard hashing, but adds that "no hashing method can fully protect a weak or reused password from being cracked."
For a company, the practical risk is reuse. If someone on your team signed up with a work email and a password they also use at work, change that work password now and confirm multi-factor login is on. Our post on whether MFA stops stolen passwords explains which methods hold up best.
One more point, and this is our advice rather than OTW's: treat any email about AO3 with care. OTW says queued notification emails, such as subscription and kudos alerts, were released and are legitimate. Even so, a well-known incident is useful cover for phishing, so do not enter a password from a link in an email.
Why a website outage like this matters for a business
Safe data did not end the outage. OTW says nothing was deleted, yet the site remains offline. A backup answers one question: can you get the data back? It does not tell you how an intruder got in, or whether the same door reopens when you restore. OTW has not explained what is taking the time, so we will not guess about AO3 specifically. For any company, though, recovery from a security incident includes investigation and cleanup, not only restoring files.
The status page kept working. OTW's status page was still posting updates, and it listed OTW's main website as operational while AO3 was down. If your website, email and customer updates all depend on one host, one incident can silence all three.
Keeping data apart limited the exposure. Because donor records sit in a separate system, OTW can tell donors something definite while account holders wait. Customer payment records, staff files and website logins benefit from the same separation.
One platform is one point of failure. AO3 readers have nowhere else to find that library. Customers are in the same position when your booking site or portal is the only way to reach you. Our posts on who to call when systems go down and why you do not own a Wix website cover that dependency, and our self-hosting and infrastructure page covers how we set systems up.
Website cyberattack recovery checklist for this week
NIST's incident response guidance treats preparation, detection, response and recovery as part of normal risk management. Its contingency planning guide and CISA's StopRansomware Guide supply the backup and planning items below. CISA wrote its guide for ransomware, but those steps fit any serious incident.
| Do this | How to check it |
|---|---|
| Set a downtime limit | Write down the longest each system can be down while the business still functions (NIST) |
| Keep offline, encrypted backups | Confirm at least one copy cannot be reached from your live network (CISA) |
| Test a restore | Restore to a clean server, time it, and repeat at least yearly (CISA, NIST sample policy) |
| Plan a clean rebuild | Confirm you can rebuild from code and configuration, without copying a possibly compromised server |
| Print the response plan | Keep a hard copy and an offline version, and rehearse it (CISA) |
| Agree a backup way to talk | Keep a phone list that does not depend on company email (CISA recommends out-of-band methods such as phone calls) |
| Host status updates elsewhere | Put your status page on a different provider from your website |
| Plan a read-only mode | Decide which features can run in a reduced state, as OTW plans to do |
| Check password storage | Ask your developer or vendor how passwords are hashed, and require MFA for admins |
| List the data you hold | Separate what you must keep, and remove what you do not need |
If you would rather have someone check these with you, our security hardening work starts with this list.
AO3 outage questions people are asking
Why is AO3 down?
OTW says it detected evidence of a security incident and is keeping the site offline while it investigates and repairs what it finds.
When will AO3 be back up?
OTW has given no date. Its estimate is a minimum of two weeks and up to four, and on November 6 it said that estimate still stands.
Was AO3 hacked?
OTW confirms a security incident but has not said how it happened or who was responsible.
Was my AO3 password stolen?
Unknown. OTW does not believe the user database was stolen but cannot rule it out. Change that password anywhere else you used it.
Did AO3 lose fan fiction or bookmarks?
OTW says no AO3 data has been deleted. It also says it is working to ensure drafts are not deleted during the outage.
Was AO3 hit by a DDoS attack?
OTW's status updates do not say so. They do not name any attack type.
The bigger lesson
It is tempting to treat recovery as the moment the backup finishes. AO3 says its data is intact and it is still offline, because getting data back is only part of getting safely back online. The time to find out how long that takes for your business is before anything goes wrong.
To pressure-test your own recovery plan, see security hardening or request a tech quote.
Get security alerts by email, with the free checklist, at our security alerts page.
Sources: OTW Status, AO3 incident; CISA StopRansomware Guide; NIST SP 800-61 Rev. 3; NIST SP 800-34 Rev. 1; AFP report via Yahoo.
Have a question about this article?
Ask it here and we will answer you directly by email. Questions are private, never posted.
Security alerts by email
Hear about the next one first.
When attackers start using a flaw in software businesses run on, we email what it is, whether it touches you and what to do that week, with a round-up of our latest security writing. Free, one-click unsubscribe. You get the checklist straight away: 12 things to secure this week.
Want a result like this?
Security alerts, breaches and the technology a business runs on: what happened, who it affects and what to do.
Get a Tech QuoteKeep reading
Aesto Data Breach: What Is Confirmed About the Healthcare Records Vendor, 4,508 South Carolina Residents, and What to Ask Your Vendors This Week
Patient records vendor Aesto says data may have been accessed or taken from its AWS systems in December 2025....
Mirae Asset Securities Data Breach: About 39,000 People Exposed, Mostly Staff, and What Finance Firms Should Check This Week
Mirae Asset Securities says two attacks on November 4 and 5 exposed data on about 39,000 people, including 35,...
NBFC Cyberattack: Two Indian Lenders Report Over Rs 7 Crore Stolen Five Days Apart as CERT-In Warns of Payment API Attacks
Spandana Sphoorty and Keerthana Finserv reported Rs 7 crore-plus in unauthorised transfers five days apart. He...
