Cisco ASA DNS Vulnerability CVE-2026-20248: A Crafted DNS Reply Can Reboot ASA and FTD Firewalls, and the Fixed Versions to Install
Cisco fixed a DNS over TCP flaw (CVE-2026-20248) that lets an attacker who can answer the firewall's DNS lookups force ASA and FTD firewalls to reload. There is no workaround. Here are the fixed versions and how to check yours.
Where Worldwide
On this page 8 sections
Cisco has fixed a flaw in its Secure Firewall ASA and Secure Firewall Threat Defense (FTD) software. An attacker can use it to force the firewall to restart by sending a specially crafted DNS reply over TCP. If your office, VPN or website runs through one of these firewalls, a restart drops every connection until the device comes back up, and no setting turns the risk off: the fix is a software upgrade.
What happened with the Cisco firewall DNS over TCP flaw
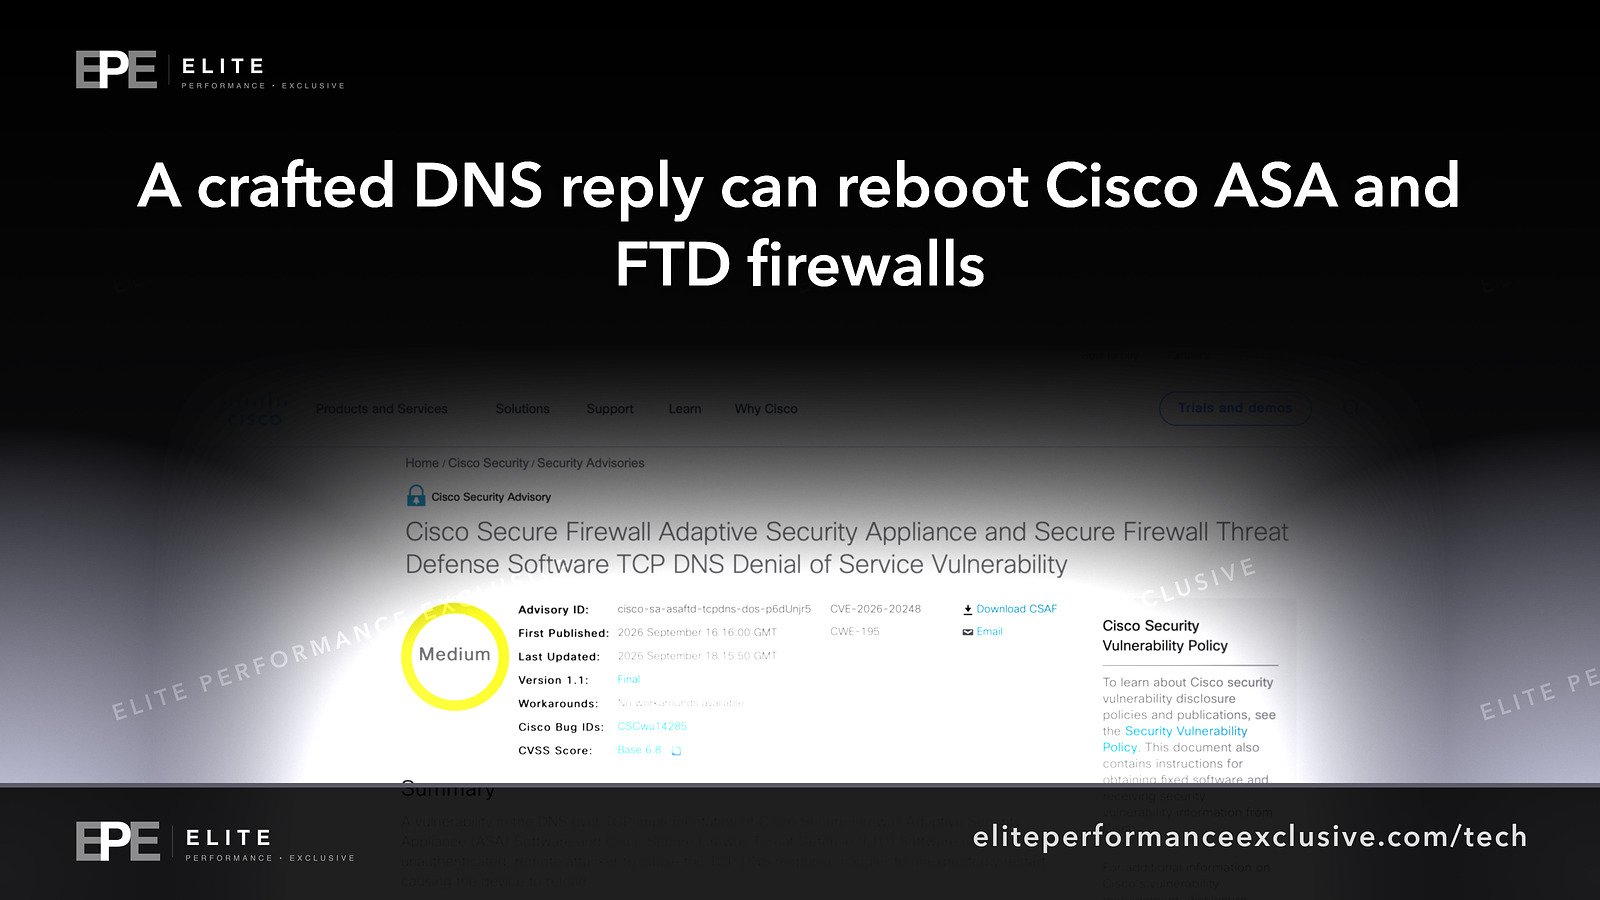
Cisco published advisory cisco-sa-asaftd-tcpdns-dos-p6dUnjr5 on Wednesday, September 16, 2026. The flaw is tracked as CVE-2026-20248 (Cisco bug ID CSCwu14285). Cisco updated the advisory on Friday, September 18, 2026 (version 1.1) to add the fixed release tables and marked it Final.
Cisco says the problem is a logic error in how the firewall's DNS over TCP code parses a DNS query and tracks incoming buffer sizes. A crafted reply can make the TCP DNS response handler restart unexpectedly, "causing the device to reload." The result is a denial of service.
The important detail is who can trigger it. According to Cisco, the attacker must be able to answer the firewall's own DNS queries. That means either controlling the DNS service the firewall uses, or sitting in a machine-in-the-middle position between the firewall and its DNS server. Going by Cisco's description, this is not a bug that anyone on the internet can set off just by sending packets to your firewall's public address.
What is confirmed and what is not known
| Confirmed by Cisco | Not known or not stated |
|---|---|
| Affects Cisco Secure Firewall ASA Software and Secure FTD Software "regardless of device configuration" | Cisco has published no technical detail beyond its summary |
| Secure Firewall Management Center (FMC) Software is not affected | Whether repeated crafted replies cause repeated reloads |
| CVSS 3.1 base score 6.8, rated Medium (CWE-195) | Whether any proof-of-concept code exists |
| No workarounds are available | How long a reload takes on your specific hardware |
| Cisco PSIRT is not aware of public announcements or malicious use | |
| Reported by Joshua Foote of the JPMorgan Chase XOR team |
The Medium rating comes mostly from the "high attack complexity" in the score, which reflects the need to control or intercept DNS answers. The impact part of the score is rated High for availability, and the scope is marked as changed. Put simply, it is hard to pull off, but if it works, the firewall goes down.
Fixed versions for Cisco ASA and FTD
Cisco Secure Firewall ASA Software
| ASA release | Affected hot fix releases | First fixed release |
|---|---|---|
| 9.16 and earlier | N/A | 9.16.4.103 |
| 9.18 | 9.18.4.135 | 9.18.4.94 |
| 9.20 | 9.20.4.235 | 9.20.4.49 |
| 9.22 | 9.22.3.191 | 9.22.3.26 |
| 9.23 | 9.23.1.195, 9.23.1.211 | 9.23.1.47 |
| 9.24 | 9.24.1.155, 9.24.1.221 | 9.24.1.26 |
Read the hot fix column carefully. A hot fix build can carry a higher number than the first fixed release and still be vulnerable. Cisco says customers who installed one of the listed hot fix releases must install the listed first fixed release.
Cisco Secure Firewall Threat Defense (FTD) Software
| FTD release | First fixed release |
|---|---|
| 7.0 and earlier | 7.0.10 |
| 7.2 | 7.2.12 |
| 7.4 | 7.4.8 |
| 7.6 | 7.6.6 |
| 7.7 | 7.7.13 |
| 10.0 | 10.0.2 |
| 10.1 | 10.1.0 |
Cisco recommends these releases because they include fixes for multiple vulnerabilities, not just this one.
Why a firewall restart matters for a business network
For most companies the firewall is the one device that everything passes through: office internet, the site-to-site link to a branch, remote staff on VPN, phones, payment terminals, and sometimes the company website or customer portal. When it reloads, all of that stops at once. Even if a restart takes only a few minutes, it can drop calls, interrupt card payments and kill active VPN sessions. Your staff will not know why.
The condition Cisco describes, an attacker who can answer the firewall's DNS lookups, is not far-fetched in every network. A compromised internal DNS server, a hijacked upstream resolver or a foothold on the network path would all put an attacker in that position. Those are also the situations where an attacker would most want to knock your firewall offline.
This is the latest in a run of Cisco firewall flaws that end in a reload. We covered a similar crash triggered by a crafted certificate in Cisco IKEv2 Vulnerability CVE-2026-20249.
The same-day Cisco firewall advisories you should not miss
This advisory was part of Cisco's September 16, 2026 publication. Cisco also released a hardening release for ASA, FTD and FMC that day (cisco-sa-hardening-asaftdfmc-uvpPROhN). Cisco rates it Critical, with CVSS scores up to 9.9. That advisory says two of the issues it groups under CVE-2026-20332 are linked to separate FMC static credential and authentication bypass advisories, and notes those two have been exploited.
The practical upshot: the first fixed ASA and FTD releases listed in the hardening advisory match the tables above, and the FTD table there also covers FMC. One planned upgrade handles both advisories, so do not upgrade the firewalls and forget the management center.
What to do this week: Cisco ASA and FTD checklist
| Step | What to do | How to check |
|---|---|---|
| 1 | List every ASA and FTD device you run, including branch sites, standby units and spares | Your asset list, FMC device inventory, or your IT provider |
| 2 | Find the running software version | show version on the ASA or FTD command line, or the device list in FMC |
| 3 | Compare against the tables above, including the hot fix column | If you run a listed hot fix build, you still need the first fixed release |
| 4 | Use the Cisco Software Checker to find one release that fixes everything | Cisco's checker offers a "Combined First Fixed" release when several advisories apply |
| 5 | Upgrade FMC as well | FMC is not affected by this DNS flaw, but it is covered by the same-day Critical hardening release |
| 6 | Schedule a maintenance window and warn staff | For high-availability pairs, follow Cisco's upgrade procedure for your release |
| 7 | Until you upgrade, review which DNS servers the firewall itself uses | Point it at resolvers you control and trust. This reduces who could answer its queries, but it is not a fix |
| 8 | Alert on unexpected reloads | Make sure syslog or monitoring tells someone when the firewall restarts |
If no one in your company owns firewall updates, that is the real gap. We wrote about it in Who Is Patching the Software That Runs Your Business?
Cisco ASA DNS vulnerability questions people are asking
What is CVE-2026-20248?
It is a denial of service flaw in the DNS over TCP code of Cisco Secure Firewall ASA and FTD software. A crafted DNS reply can make the firewall reload.
Can someone on the internet crash my Cisco firewall with this?
Not just by sending traffic to it, according to Cisco. The attacker has to be able to answer the firewall's own DNS queries, either by controlling its DNS server or by intercepting the traffic.
Is the Cisco firewall DNS flaw being exploited?
Cisco says its PSIRT is not aware of any public announcements or malicious use of this vulnerability.
Is there a workaround for CVE-2026-20248?
No. Cisco says there are no workarounds. Upgrading to a fixed release is the only fix.
Does it depend on my firewall configuration?
No. Cisco says ASA and FTD software were affected regardless of device configuration.
Is Cisco Firewall Management Center affected?
Not by this flaw. Cisco confirmed FMC is not affected. FMC is covered by the separate Critical hardening release published the same day.
Which version fixes the Cisco ASA DNS vulnerability?
For ASA, for example, 9.20.4.49, 9.22.3.26 or 9.24.1.26, depending on your release line. For FTD, 7.2.12, 7.4.8, 7.6.6, 7.7.13, 10.0.2 or 10.1.0. Check the full tables above.
Are Meraki or other Cisco firewalls affected?
The advisory lists only ASA and FTD software. Cisco says only products listed as vulnerable are known to be affected.
The bigger lesson
A Medium rating does not mean a minor outcome. When the flaw sits in the one box every connection passes through, "hard to exploit" still ends in "everything is offline." The businesses that come through these advisories without trouble know what firewalls they run and which versions they are on, and they have an upgrade window already on the calendar.
Want your firewalls inventoried, patched and monitored? See security hardening or request a quote.
Get security alerts like this by email, plus our free checklist, at /security-alerts.
Sources: Cisco Security Advisory: ASA and FTD TCP DNS Denial of Service Vulnerability; Cisco Security Advisory: ASA, FTD and FMC Software Hardening Release, September 2026.
Have a question about this article?
Ask it here and we will answer you directly by email. Questions are private, never posted.
Security alerts by email
Hear about the next one first.
When attackers start using a flaw in software businesses run on, we email what it is, whether it touches you and what to do that week, with a round-up of our latest security writing. Free, one-click unsubscribe. You get the checklist straight away: 12 things to secure this week.
Want a result like this?
Security alerts, breaches and the technology a business runs on: what happened, who it affects and what to do.
Get a Tech QuoteKeep reading
Refrigeration Controller Hacks: CISA and FBI Warn Cold-Chain Businesses, What Is Confirmed and the Danfoss Firmware to Check
US agencies say attackers are targeting refrigeration and cold-chain controllers after two waves of store atta...
Cold Chain Cyberattacks: FBI and CISA Warn Refrigeration Controllers Are Being Targeted, What France Confirmed and What to Check This Week
Attackers changed refrigeration settings at about 700 French retail sites in October, and US agencies now urge...
Plex2Shell QNAP NAS Exploit: Attackers Compromise Plex Media Server on NAS Devices, the Fixed Version and How to Check Yours
QNAP says attackers have compromised Plex Media Server on some NAS devices using Plex2Shell, a four-flaw chain...
