Security & Technology
Security alerts, breaches and the technology a business runs on: what happened, who it affects and what to do.
Lovable Data Leak: Apps Built on Lovable Exposed Passport Details and 200,000 Chat Messages, What Is Confirmed and What to Check
Researchers found thousands of Lovable-built apps handing out database records with no login, including passport numbers and 200,000 chat messages. Here is what is confirmed, what is not, and what to check this week.

Residential Proxy on Employee Devices: The White House Network Was for Rent, and How to Check Yours
Researchers say White House internet addresses could be rented through residential proxy services for a month. Here is what is confirmed, what is not, and how to check whether your office network is being rented out too.

iCloud Shared Link Scanning: Apple Will Check 'Anyone with the Link' Files and Photos From iOS 27.3, What Is Confirmed and What Businesses Should Change
Apple says iCloud photos and files shared with Anyone with the Link will be checked for harmful content starting in iOS 27.3. Here is what is confirmed, what is not, and how to tighten sharing this week.
GhostMap Android Flaw: A No-Permission App Can Trap Phones in a Boot Loop, No Patch Yet, and How to Lock Down App Installs
Bitdefender says a crafted Android app with no permissions can trap a phone in an endless boot loop as soon as it is installed. Google says it will not fix this in a security update. Here is what is confirmed and how to control installs on company phones.
OpenAI Linux Kernel Exploits: AI Found 948 Root Flaws in One Run, What Is Confirmed and What Linux Servers Need This Week
OpenAI says its unreleased cyber AI model found and exploited 948 distinct Linux kernel root flaws in one $1.2 million run. Here is what is confirmed, what is not, and how to check your Linux servers.

Cisco UCS Central Vulnerability CVE-2026-76506: Logged-In Users Could Run Commands on Your Server Management Console, Update to 2.1(2c)
Cisco has fixed CVE-2026-76506, a high-severity flaw in UCS Central Software. Anyone with a low-privileged login could run commands, write files or read sensitive data. There is no workaround, and the fix is 2.1(2c).
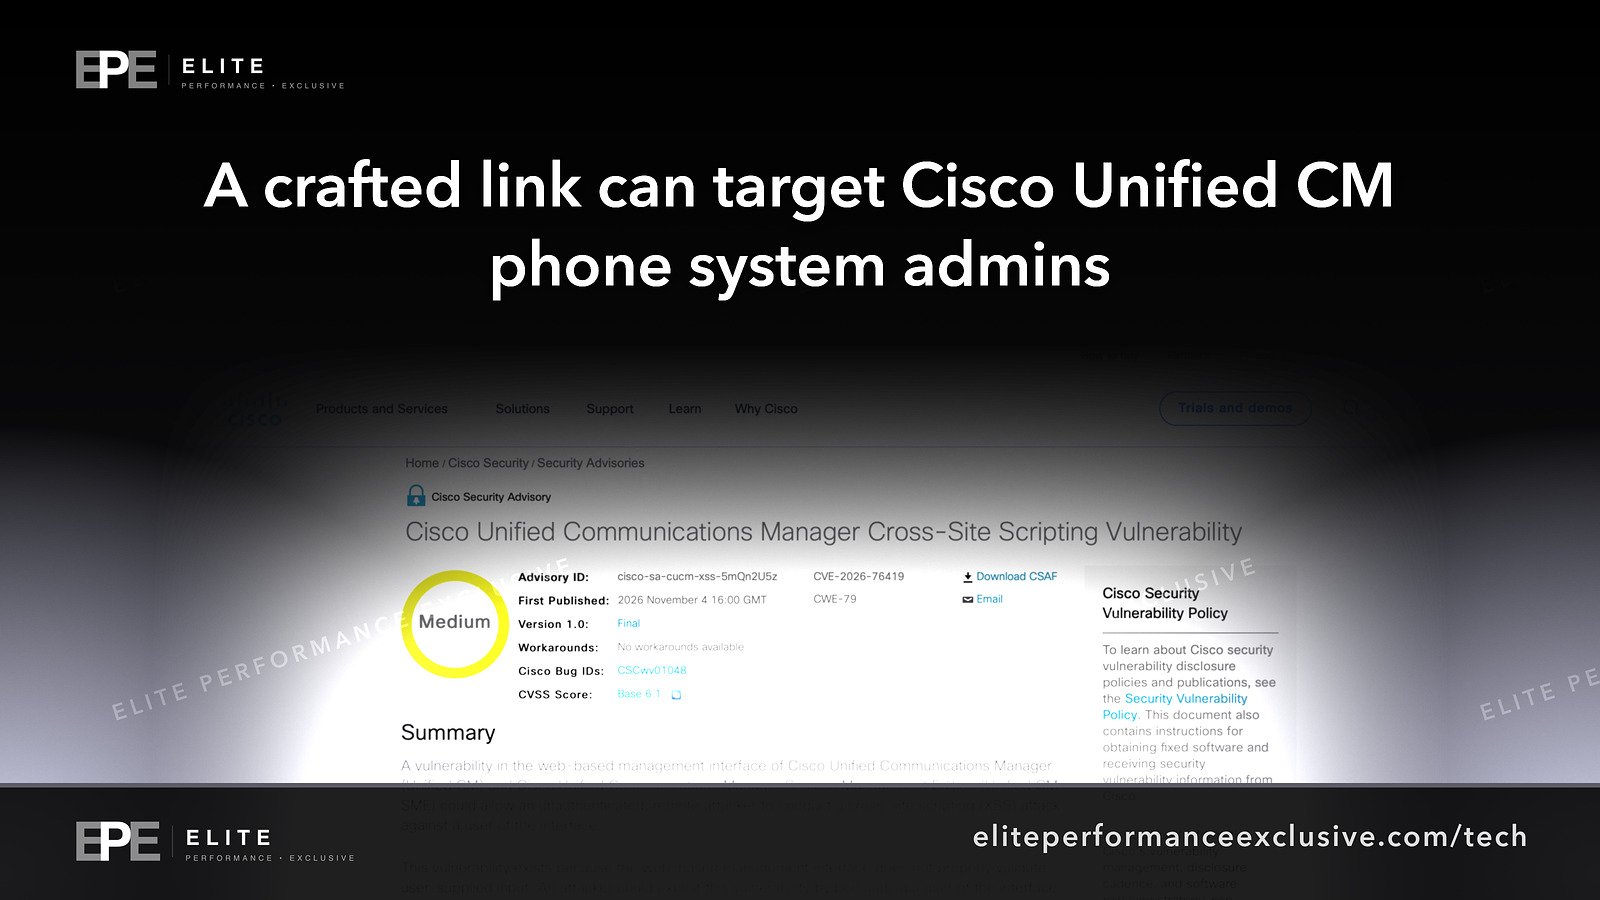
Cisco UCM XSS Vulnerability CVE-2026-76419: A Crafted Link Can Target Phone System Admins, No Workaround, and Why Release 14 Must Move to 15SU5
Cisco has fixed CVE-2026-76419, a cross-site scripting flaw in the Unified CM and Unified CM SME web management interface. There is no workaround. Release 15 is fixed in 15SU5, and Release 14 has no patch of its own.
Cisco ISE Vulnerability CVE-2026-20241: Attackers With No Login Can Obtain Endpoint Identity Certificates, and the Patch Level to Check
Cisco says a flaw in ISE and ISE-PIC lets an attacker with no login obtain an endpoint identity certificate. There is no workaround. Here are the fixed patches and how to check yours.

Vercel Device Bound Session Credentials: How DBSC Makes Stolen Session Cookies Useless, What Is Confirmed and What to Check
Vercel's CTO says Vercel is rolling out Device Bound Session Credentials (DBSC) for vercel.com logins. This ties sessions to the device so cookies stolen by malware stop working elsewhere. Here is what is confirmed and what to check.
