Apache HTTP Server Vulnerability CVE-2026-119618: mod_http2 Flaw Reportedly Exploited, Fixed in 2.4.71, and How to Check Your Version
Apache says a mod_http2 flaw in HTTP Server 2.4.55 through 2.4.70 can lead to remote code execution, and Singapore's CSA says it is reportedly being exploited. Here is what is confirmed and how to get to 2.4.71.
Where Worldwide
On this page 9 sections
Apache has fixed a flaw in Apache HTTP Server, tracked as CVE-2026-119618. Apache's own security notice says it can lead to remote code execution (RCE), which means an attacker could run their own code on your server. Singapore's Cyber Security Agency (CSA) says the flaw is reportedly being exploited and that a proof-of-concept exploit is public. If a website, web app or customer portal of yours runs Apache HTTP Server 2.4.55 through 2.4.70, put the update to 2.4.71 on this week's list.
What happened with CVE-2026-119618
The bug is in mod_http2, a module of Apache HTTP Server, inside a function called assign_headers(). Apache's notice describes it like this: "Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead to RCE."
In plain terms, it is a timing problem, also called a race condition. Two parts of the server work on the same data at the same time without proper coordination. Apache says this mistake can be pushed far enough to run code on the server.
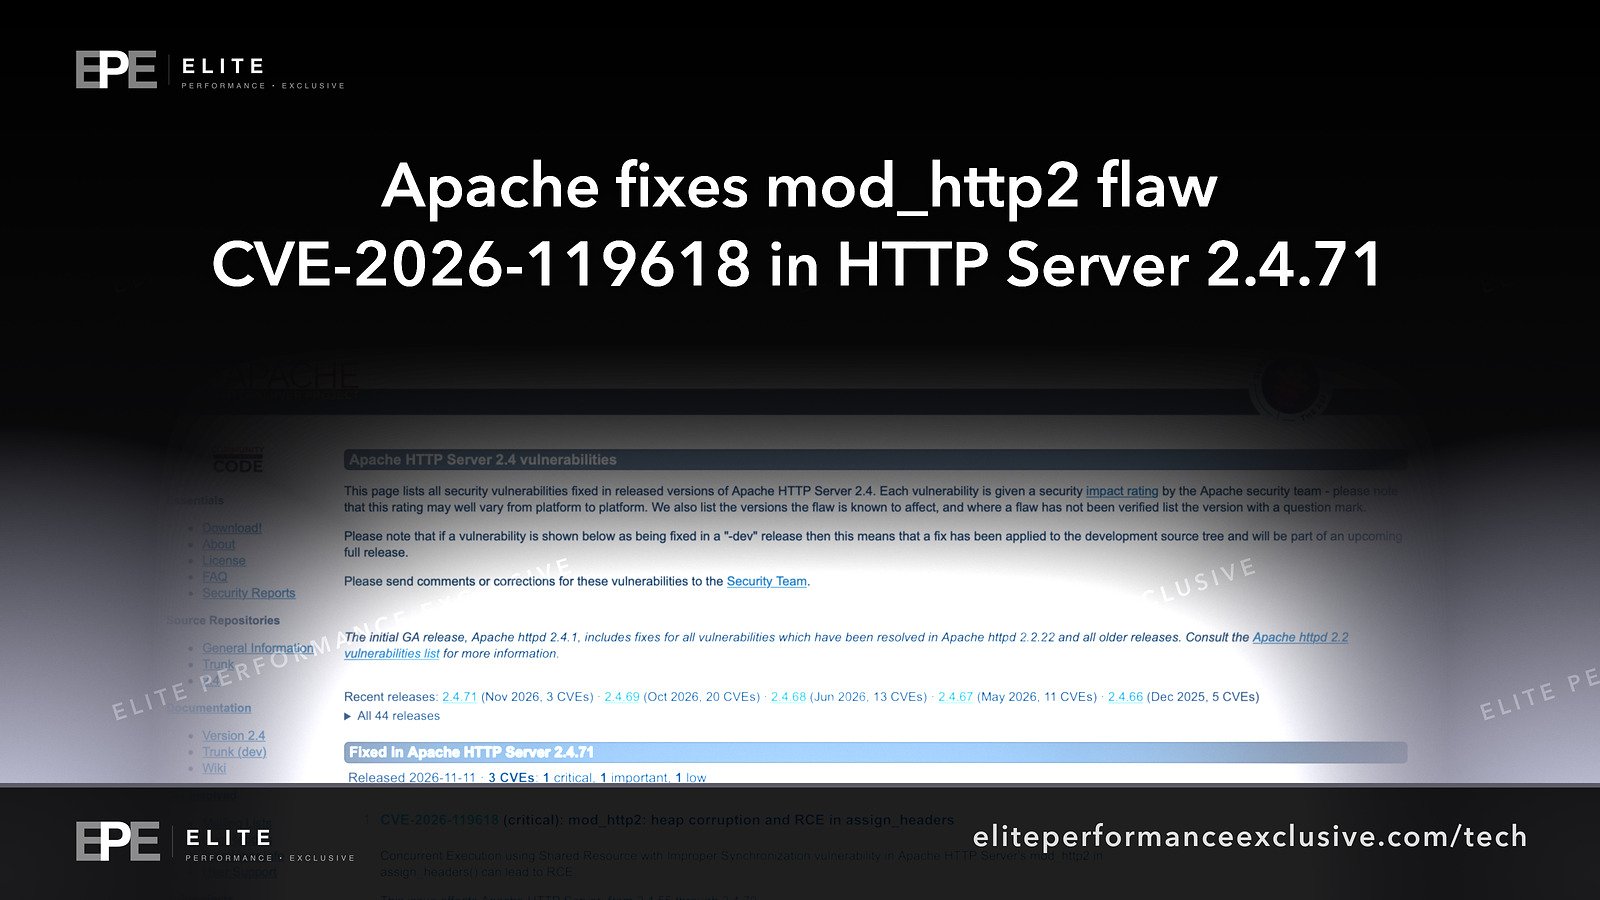
Apache released the fix in version 2.4.71 on 2026-11-11 (November 11, 2026). Apache credits the discovery to Anthropic's OSS Scanner, which reported it as vulnerability ANT-2026-MAPKT6MZ.
What is confirmed and what is claimed
| Point | Status | Where it comes from |
|---|---|---|
| A flaw in mod_http2's assign_headers() can lead to RCE | Confirmed by the vendor | Apache security notice |
| Affects Apache HTTP Server 2.4.55 through 2.4.70 | Confirmed by the vendor | Apache security notice |
| Fixed in 2.4.71, released 2026-11-11 | Confirmed by the vendor | Apache security notice |
| CVSS v3.1 score of 8.1 out of 10 | Stated by the CSA | CSA alert |
| Actively exploited | Reported: the CSA says "reportedly" | CSA alert |
| A proof-of-concept exploit is public | Stated by the CSA | CSA alert |
What is not known. The sources we checked do not say who is exploiting the flaw or which organizations have been hit. They do not say whether an attacker needs to log in first or can reach the flaw from the open internet without an account. They do not describe any workaround short of updating. They also do not say whether a server without mod_http2 loaded is safe. Until someone publishes those answers, treat them as unknown and do not plan around them.
Which Apache versions are affected
Apache's notice is specific: "This issue affects Apache HTTP Server: from 2.4.55 through 2.4.70."
- 2.4.55 through 2.4.70: affected by CVE-2026-119618.
- 2.4.71: the release that fixes it.
- Older than 2.4.55: this notice does not list them for this CVE. That does not make an old server a good place to stay. The CSA's advice is to update to the latest versions.
Is CVE-2026-119618 being exploited?
The CSA alert says: "This vulnerability is reportedly being actively exploited, and a proof-of-concept exploit is publicly available."
Notice the word "reportedly". The CSA is reporting that attacks are happening, but it has not published who was attacked or how. None of our sources describe the attacks in detail. The public proof-of-concept matters either way: working code that demonstrates the flaw is now available to anyone who goes looking for it, which makes it easier for attackers to try.
How to check your Apache version
- Check the version. On each server, run
httpd -v,apache2 -vorapachectl -v(the command name depends on the system). Then read the number after "Apache/". - See whether mod_http2 is loaded. Run
apachectl -Mand look forhttp2_module. This tells you where the affected module is in use, but update either way. The sources do not say that servers without the module are safe. - Do not rely on the number alone for packaged builds. If Apache comes from your operating system's packages, a hosting control panel or a managed host, ask the supplier to confirm that their build includes the fix for CVE-2026-119618.
- Look beyond the main website. Your inventory should include staging servers, old test machines, internal tools and any container images or vendor products that bundle Apache HTTP Server.
What to do this week
| Task | How | Done when |
|---|---|---|
| List every Apache HTTP Server | Go through servers, virtual machines, containers and hosted sites | You have a list with each version |
| Flag affected versions | Use the version commands above | Every server is marked as either 2.4.55 to 2.4.70 or not |
| Update to 2.4.71 or later | Use your package manager, control panel or Apache's own release | The version shows 2.4.71 or later, or the supplier confirms the fix in writing |
| Restart and test | Restart Apache, load the site and check the error log | The site works on the new version |
| Ask your hosts and vendors | Email them and name CVE-2026-119618 | You have a written answer with a date |
| Review servers that ran affected versions | Look for unexpected processes, new files and unfamiliar accounts | The review is done and anything odd is escalated |
The sources do not publish signs of compromise for this flaw. The last row is general good practice, not a specific detection method.
Why it matters for a business website or network
For most businesses, the web server is the most exposed machine they run. Customers and the public reach it every day. If attackers can run their own code on it, they could get at the website's files, the passwords it uses to reach its database and any internal systems the server can talk to. A flaw like this goes beyond defaced pages. It can be how attackers get in.
The second risk is ownership. Many companies do not know which Apache version their site runs, or who is responsible for updating it. Sometimes it is the host, sometimes a former developer, sometimes nobody. If you run your own servers, our self-hosting and infrastructure page explains how we set up patching from the start.
Apache CVE-2026-119618 questions people are asking
What Apache version fixes CVE-2026-119618?
Apache HTTP Server 2.4.71, which Apache released on 2026-11-11.
Is Apache 2.4.70 vulnerable?
Yes. Apache lists versions 2.4.55 through 2.4.70 as affected.
How serious is the mod_http2 RCE?
The CSA gives it a CVSS v3.1 score of 8.1 out of 10. Apache says it can lead to remote code execution. The CSA says it is reportedly being exploited and that a proof-of-concept exploit is public.
Is there a workaround if I cannot update right away?
None of the sources we checked describe one. Plan the update to 2.4.71 instead of waiting for a workaround.
Can attackers exploit it without logging in?
The sources do not say. Treat this as unknown, not as a reason to wait.
Who found the Apache mod_http2 flaw?
Apache credits Anthropic's OSS Scanner, which reported it as vulnerability ANT-2026-MAPKT6MZ.
My website is on a hosting plan. Am I affected?
Possibly, if your host runs Apache HTTP Server 2.4.55 through 2.4.70. Ask your host directly whether your server has the fix for CVE-2026-119618, and get the answer in writing.
The bigger lesson
The fix only protects servers where someone actually installs it. That only happens if you know which software runs your website, which version it is on and who is responsible for updating it. Write those three things down for every server this week. The next advisory will then take you an afternoon instead of a scramble.
To have your servers and sites checked and kept patched, see security hardening or get a quote.
Get security alerts like this by email, plus our free checklist, at security alerts.
Sources: Apache security notice; CSA Singapore alert.
Have a question about this article?
Ask it here and we will answer you directly by email. Questions are private, never posted.
Security alerts by email
Hear about the next one first.
When attackers start using a flaw in software businesses run on, we email what it is, whether it touches you and what to do that week, with a round-up of our latest security writing. Free, one-click unsubscribe. You get the checklist straight away: 12 things to secure this week.
Want a result like this?
Security alerts, breaches and the technology a business runs on: what happened, who it affects and what to do.
Get a Tech QuoteKeep reading
Automated AI Cyberattack: Google Finds exploit_agent Turning Software Patches Into Live Attacks With No Human in the Loop, and What to Do This Week
Google says attackers used an AI framework called exploit_agent to find and exploit flaws in popular web softw...
SignDrop Windows Zero-Day: Public Exploit Claims SYSTEM Access Through CLFS, No Microsoft Patch or CVE Yet, and What to Do This Week
A researcher has published SignDrop, exploit code they say turns a normal Windows login into full SYSTEM contr...
TSMC Data Breach: 46,000 Employee Records Reportedly for Sale, TSMC Finds No Evidence Its Systems Were Hit, and What to Check at Your Own Vendors
Anonymous sellers reportedly offered 46,000 TSMC employee records for three Bitcoins. TSMC says it found no ev...
